Product Four modules, one evidence record
Readiness for four frameworks, evidence you can defend
ProveStack guides your team through each requirement, records the decisions people make and keeps the evidence behind them. Screenshots show the running product with fictional data; capabilities not delivered yet carry their status and are never mocked up.
Available in the pilot today On request set up with you In development not usable yet
01 Cyber Resilience Act
CRA readiness for each product you ship
- AvailablePreliminary CRA orientation per product and an obligation catalogue with legal references and dates; a person records each applicability decision with a rationale.
- AvailableInventory: releases with support periods, CycloneDX JSON SBOM import with source hash, import from GitHub per release.
- AvailableAdvisories and exploited vulnerabilities: OSV import with explainable matching, CISA KEV and ENISA EUVD feeds, guided checks you run yourself.
- AvailableReporting preparation: early warning, notification and final report deadlines from the time you became aware; a person submits through the ENISA platform.
The public demo walks through this CRA journey with fictional data.
02 ISO/IEC 27001
An ISMS you can explain, control by control
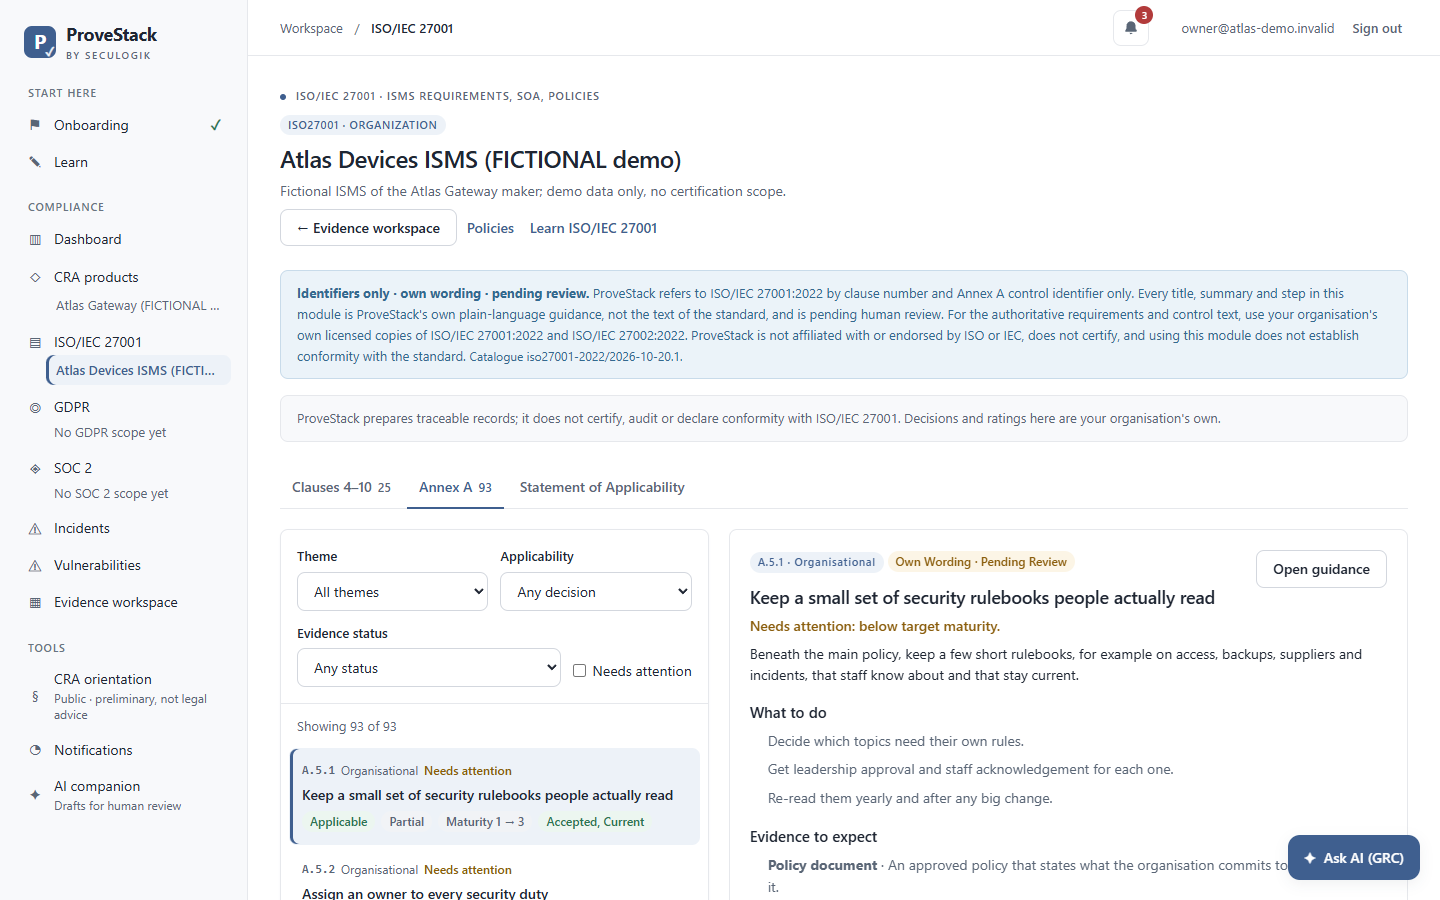
- AvailableClauses 4 to 10 and Annex A, referenced by identifier, with titles, summaries and steps in our own words: you need your own licensed copy of the standard.
- AvailableStatement of Applicability and target and achieved maturity per control.
03 GDPR
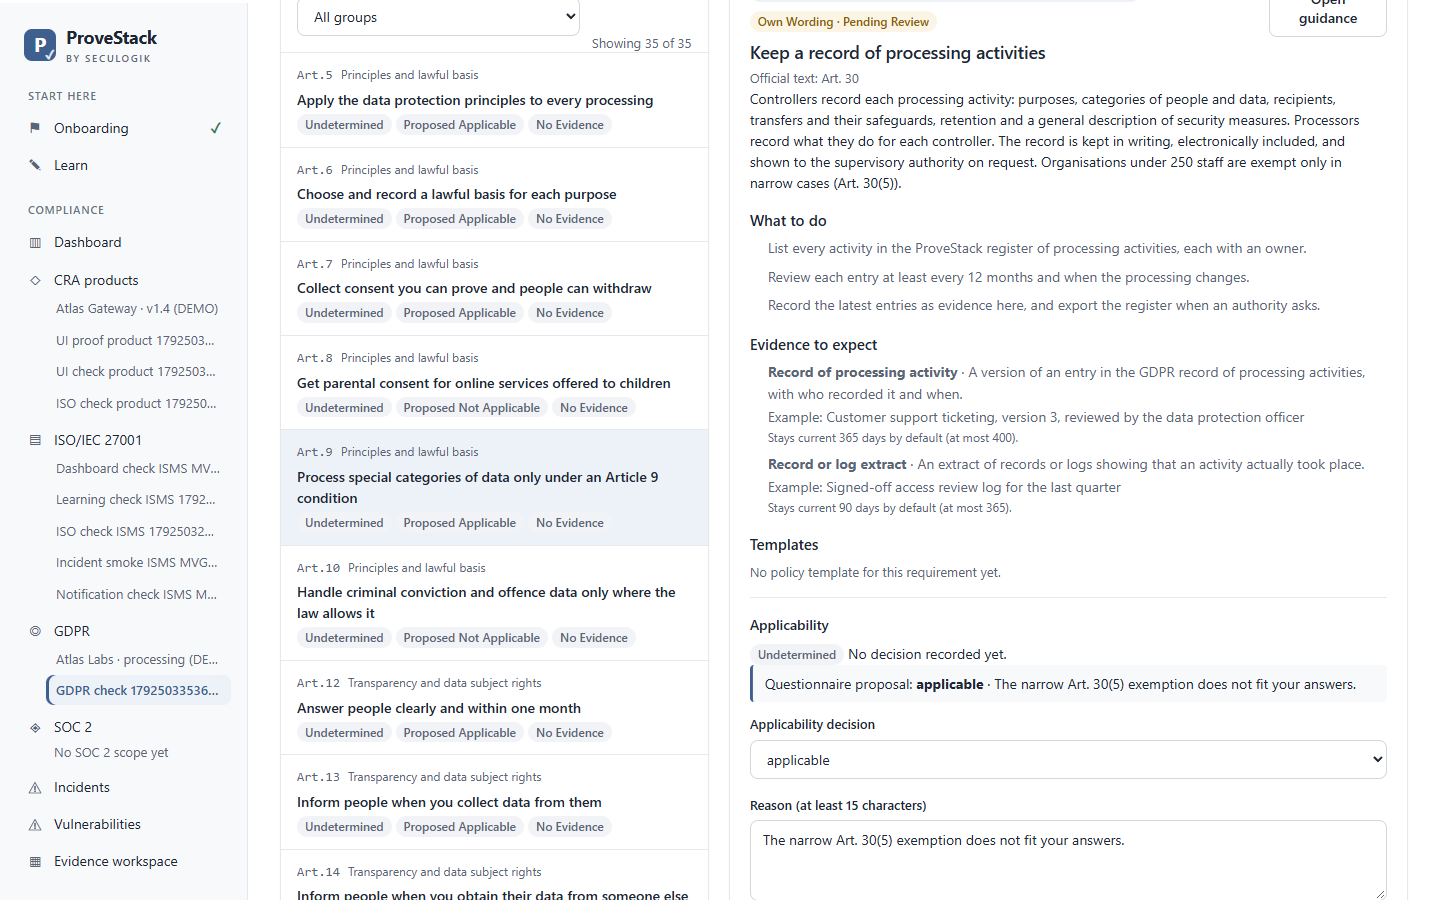
35 requirements and your record of processing
- AvailableApplicability questionnaire that proposes a decision for each of the 35 requirements; a person confirms it with a reason.
- AvailableRecord of processing activities, versioned, with an owner per activity and an export for the authority.
04 SOC 2
Type 1 and Type 2 readiness
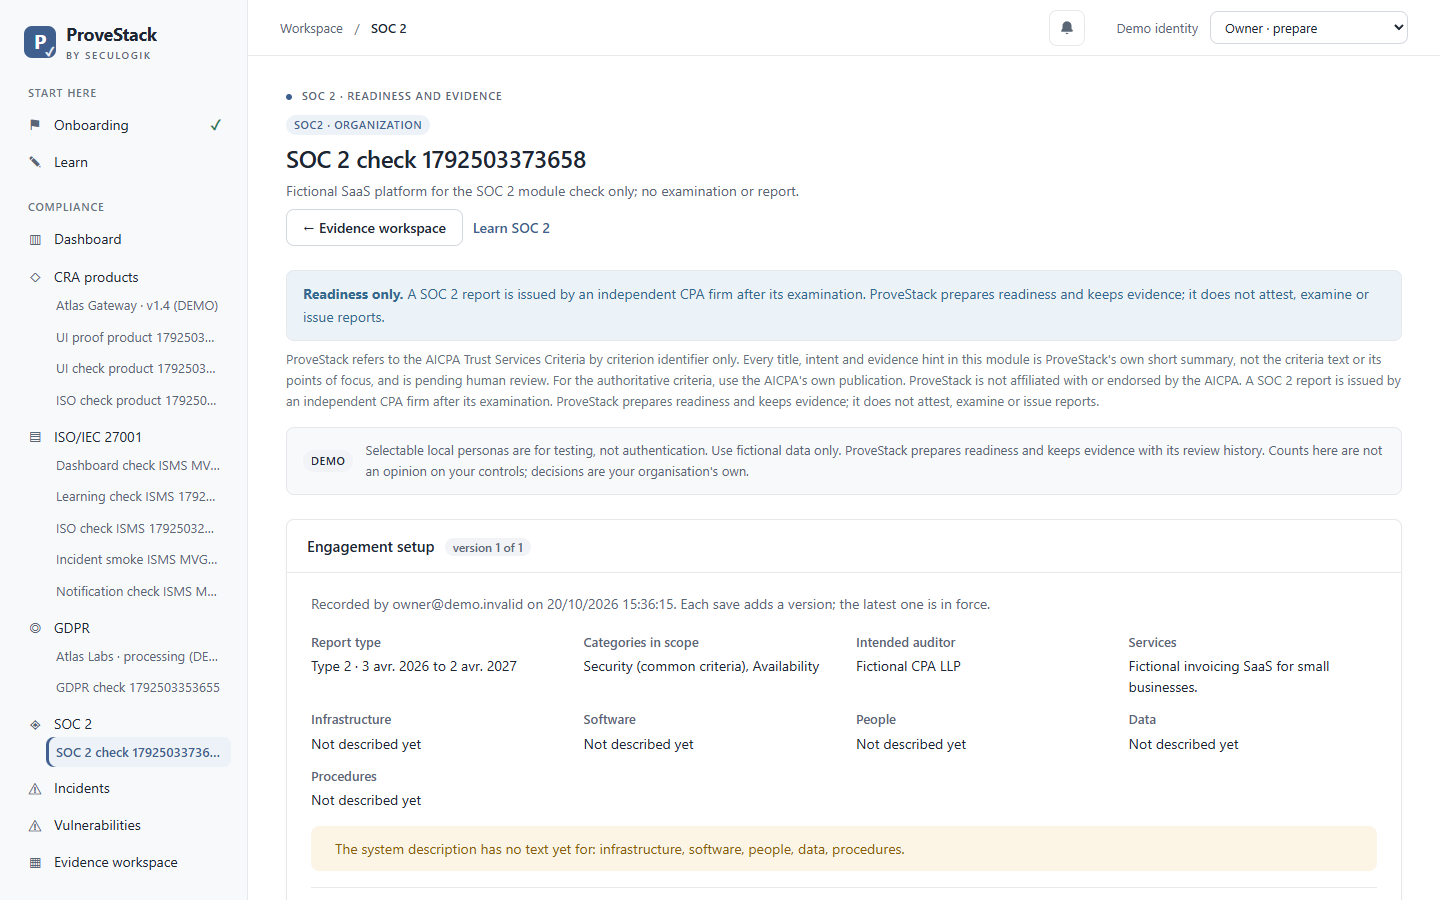
- Available61 criteria referenced by identifier, the engagement setup and the system description.
- AvailableObservation-period coverage for Type 2: which evidence covers which part of the period.
A SOC 2 report is issued by an independent CPA firm after its examination. ProveStack prepares readiness and keeps evidence; it does not attest.
05 Operations
Incidents, vulnerabilities and the clocks behind them
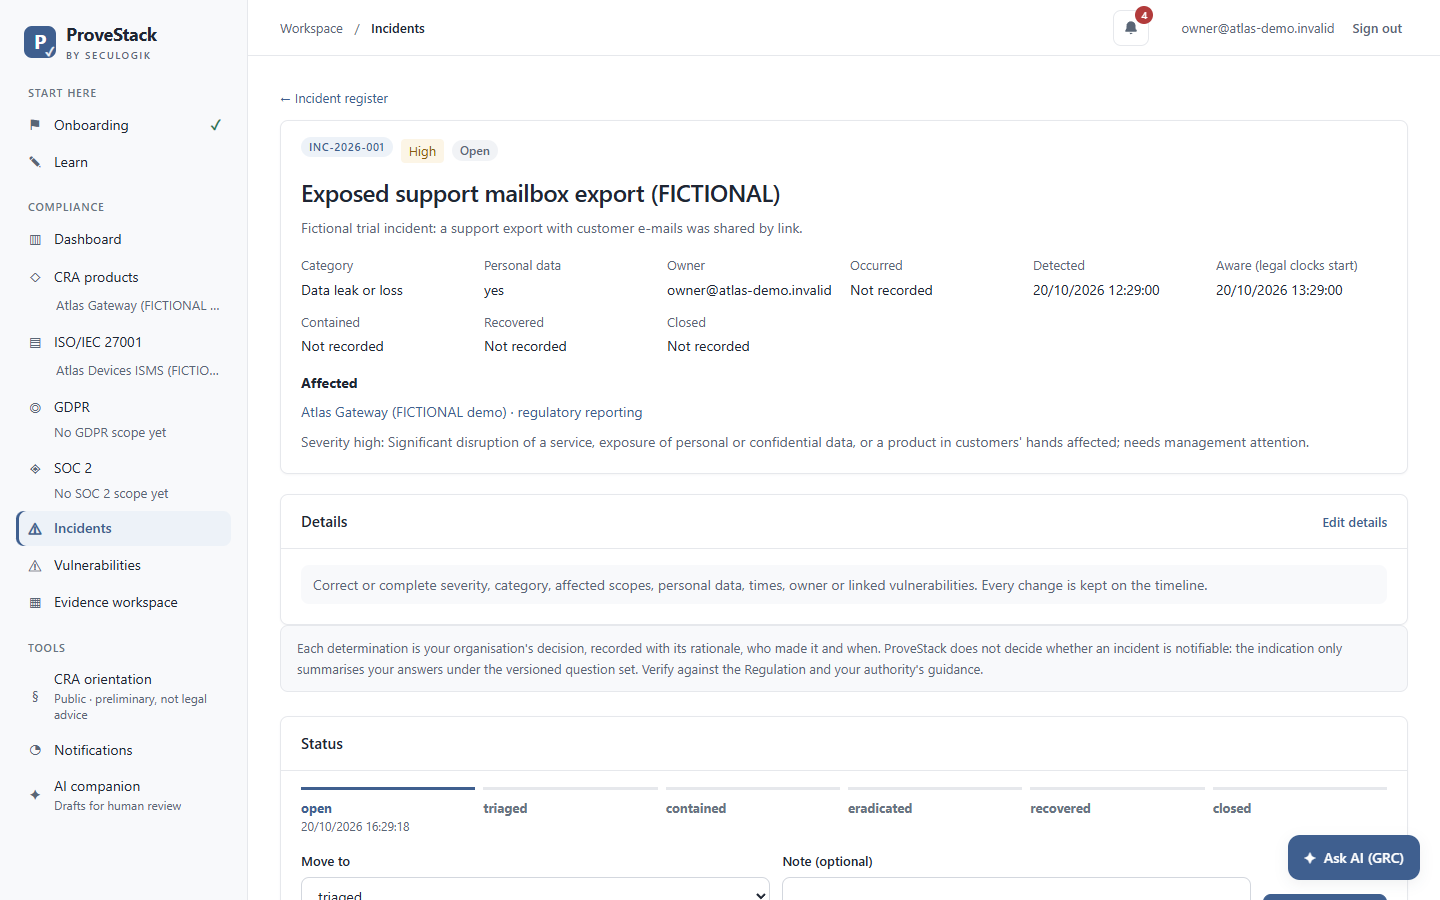
- AvailableIncident management: CRA Article 14 and GDPR Articles 33 and 34 notification decisions and deadlines. ProveStack does not decide whether an incident is notifiable; a person does, with a recorded rationale.
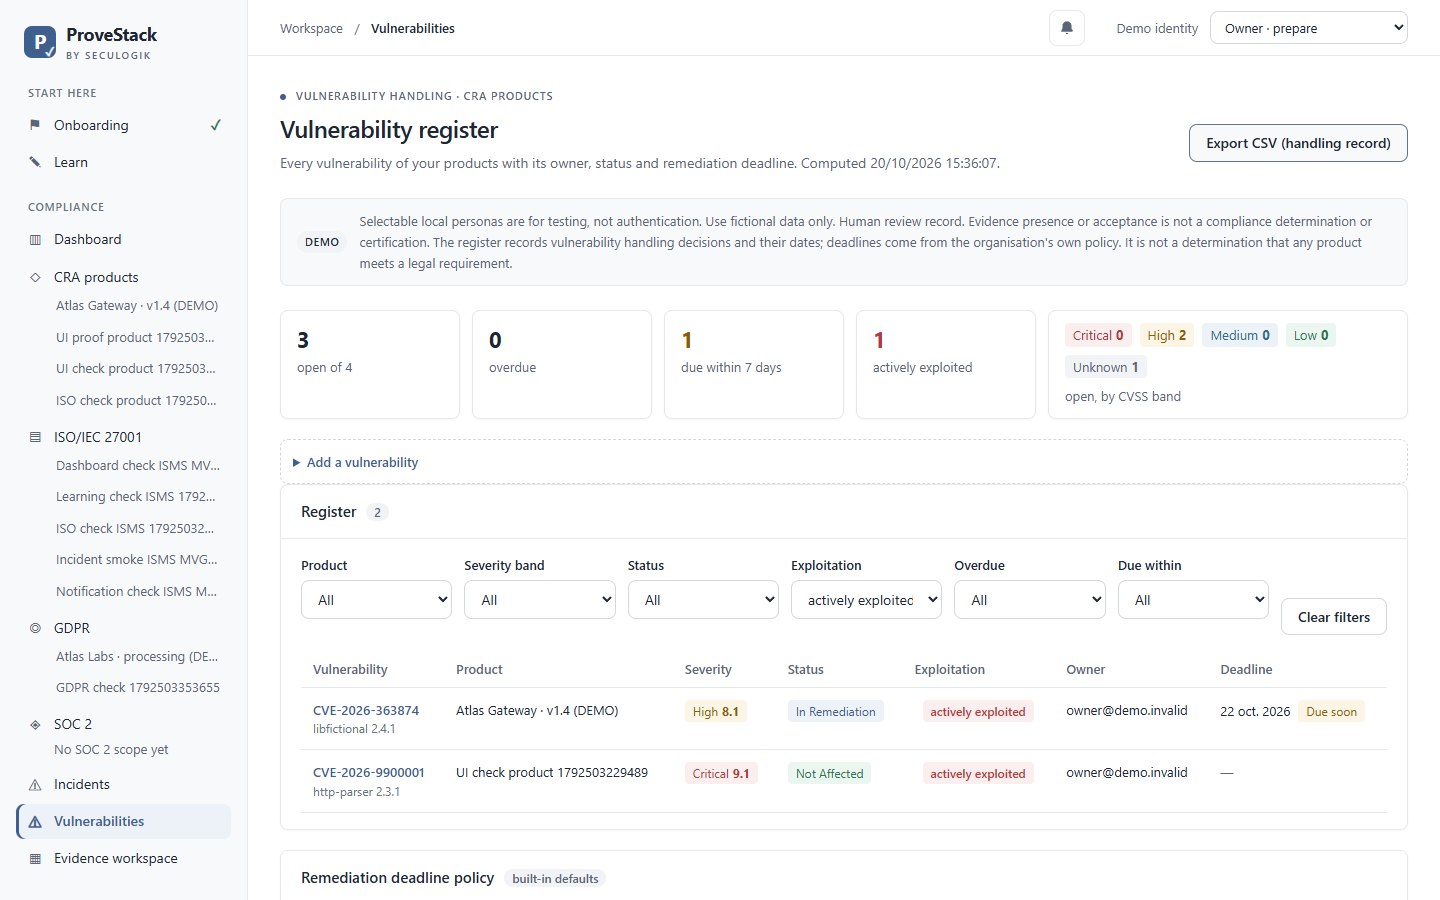
- AvailableVulnerability tracking: remediation deadlines from your own policy, history, the CRA reporting path for actively exploited ones.
- AvailableNotification centre, with optional e-mail.
06 Across modules
One evidence engine
- AvailableLearning journey led by documentation, with knowledge checks, and guidance for every requirement.
- AvailableEvidence files stored with their SHA-256, write-once; independent review of each version, no self-approval.
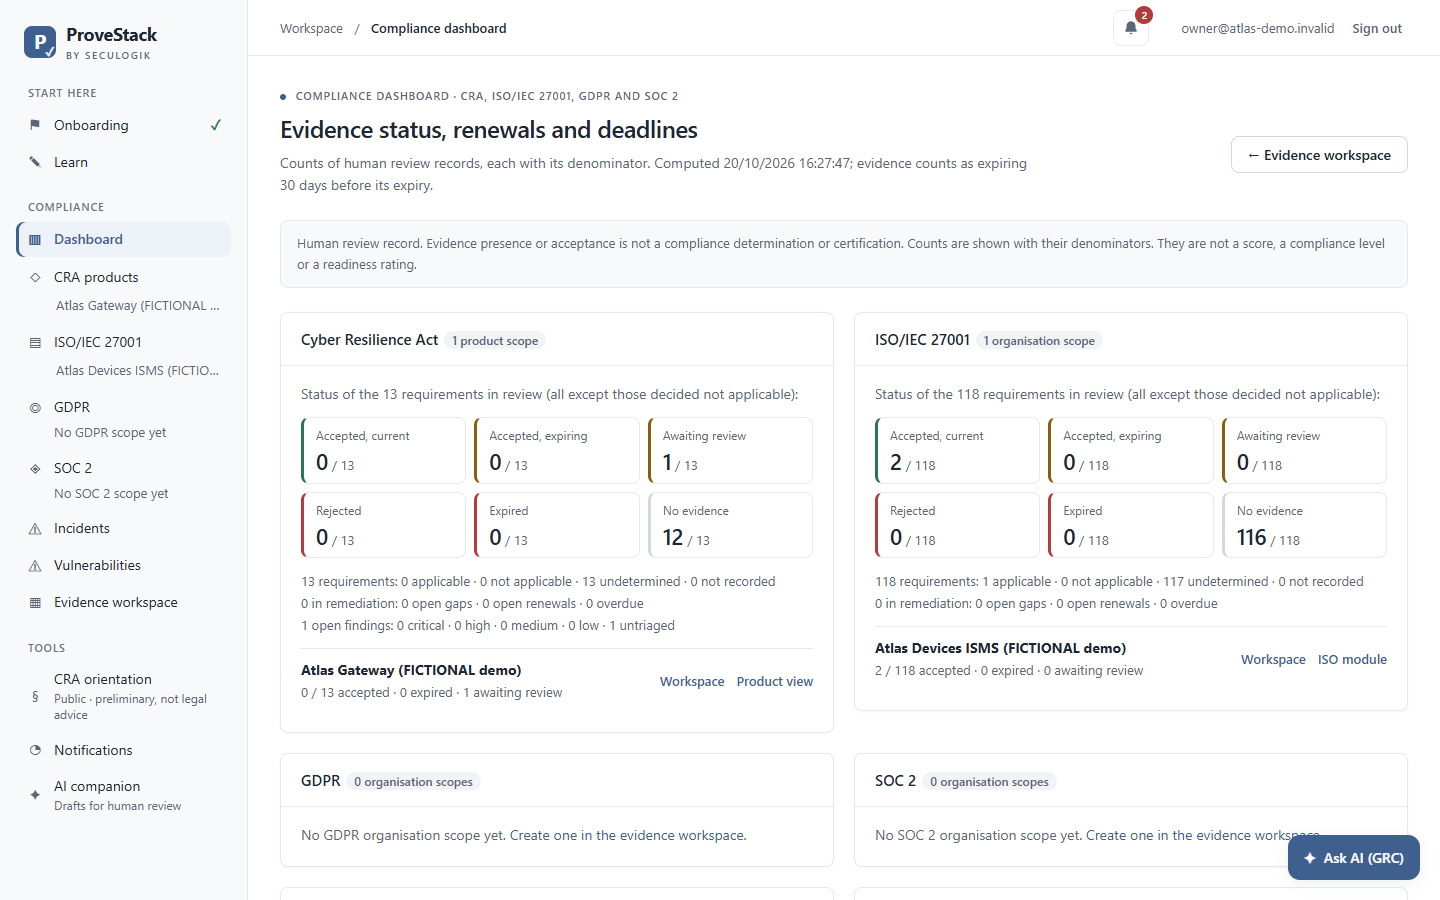
- AvailableExpiry and renewal, and a dashboard with denominators: counts of reviewed records, never a compliance percentage.
- AvailableAuditor packet export with evidence, decisions, journal and open items.
- In developmentEncrypted, immutable vault with retention lock and SHA-256 verified on every read, and a cold archive for older evidence.
07 Add-on
AI companion, for drafts a person reviews
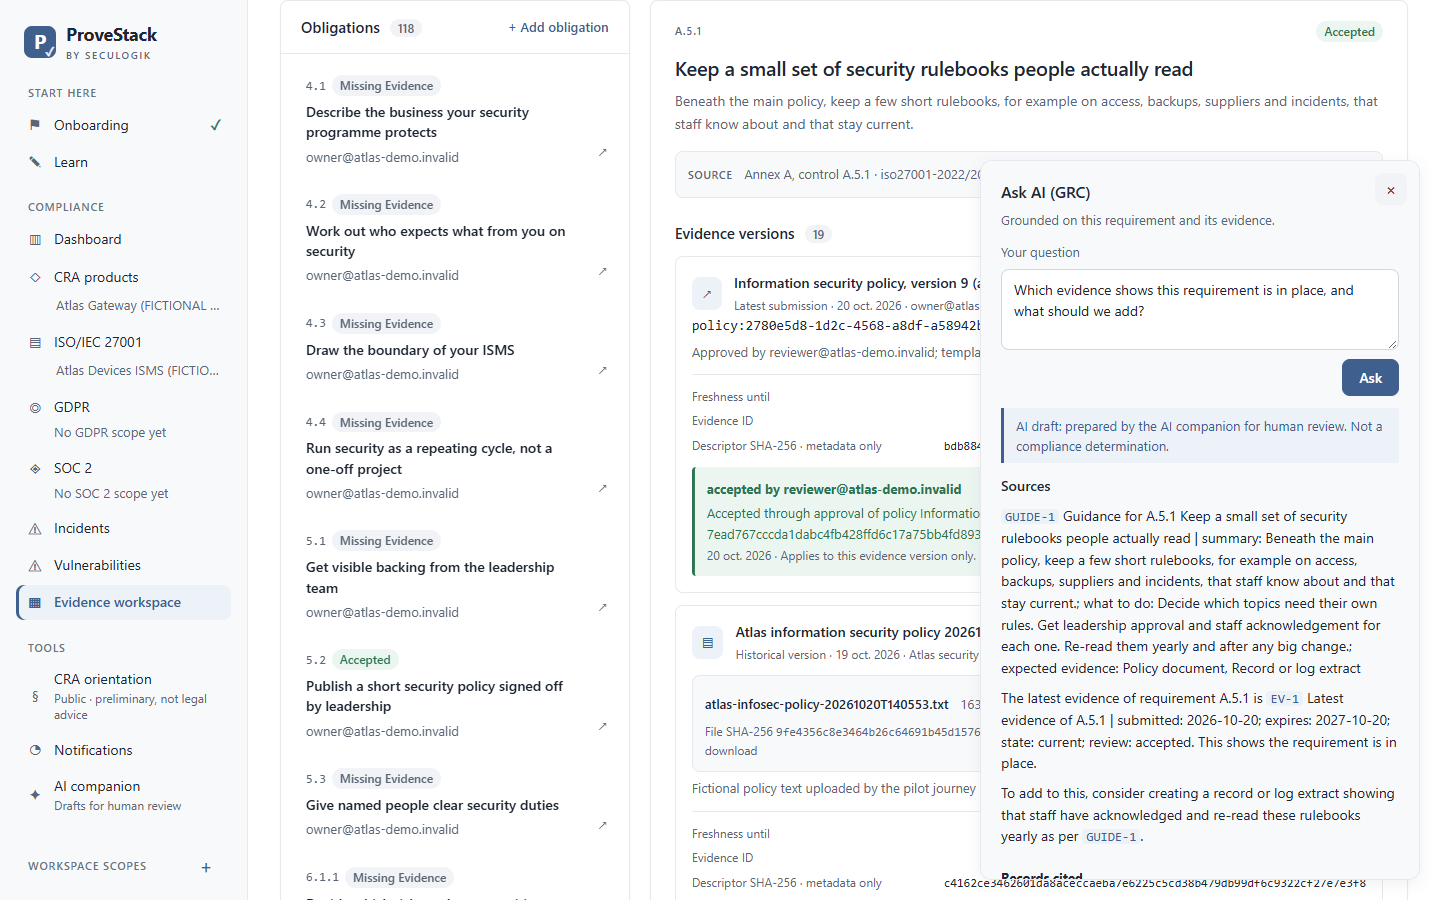
- On requestAsk AI about a requirement and its evidence, and GRC skills that prepare drafts. Every answer cites its sources, is watermarked, and is never applied automatically.
- On requestModel served through Ollama: hosted (drafts are computed by a third-party model provider) or, on premises, a local model.
See it on your own scope
A pilot runs ProveStack on your instance with your people. Prices are public; pilot terms on request.